Fairway
Fairway and Virtus§101.630(f)

Two firms, one program. The rule wants it that way.

Fairway Systems and Virtus Cybersecurity deliver every program together. Here is why a compliance program needs two firms, and who leads what.


Why two firms

Nobody marks their own homework here

Every Cybersecurity Plan under 33 CFR Part 101 Subpart F carries an annual obligation that most operators skim past on the first read: the plan has to be audited every year, and the audit has to be done by someone independent of the measures being audited. Your Cybersecurity Officer cannot audit their own program. Neither can the firm that wrote it, if the same people who wrote it are the ones checking it.

That one sentence decides how a compliance program has to be built. A compliance shop without a security bench is a paperwork vendor. A security firm without the rule and the market is selling into a room it has never been in. So ours is delivered by two firms, each leading what it is best at, and we think that is worth explaining rather than tucking into a footnote.


Who leads what

The same words, on both firms' sites

Fairway Systems leads the program: the rule, the fourteen-section Cybersecurity Plan, the Cybersecurity Officer of record, the portal and the calendar.

Virtus Cybersecurity leads the security work: the assessment, penetration testing, incident response, the technical build of the plan, and the annual independent audit.

One contract, one fixed quote, and two firms each doing what they are best at.

Fairway leads
The rule and the market
Research, the content library, this site, the webinars, the trade press, the associations and the shows. Everything that turns a regulation into a path a fleet can walk.
Your program and your quote
The proposal, the fixed itemized quote, the contract, the project management and the person you call. One name on the engagement, start to finish.
The Cybersecurity Officer of record
Named in your plan, reachable when the Coast Guard calls, and running the calendar of every date the rule creates: training, drills, amendments, the audit.
The portal and the documents
The fourteen sections assembled, the records designed to survive an inspection, and the waiver filing reviewed by maritime counsel when that is the right lane.
Virtus leads
The Cybersecurity Assessment
The technical assessment against the Coast Guard's own method: asset inventory, vulnerabilities, findings and risk analysis, on the maritime asset classes Fairway supplies.
The technical build of the plan
The sections on security measures: access control, segmentation and remote access, monitoring and logging, patching, and the incident response plan. Then a quality review of the whole before it carries either name.
The alternate officer and the on-call bench
A named alternate Cybersecurity Officer, the after-hours first ring, and hands-on incident response and forensics when something actually happens.
Penetration testing and the annual audit
The penetration test the rule requires at the five-year renewal, and every annual audit, performed by people who did not build or run the measures they are checking.

Together: every kickoff, the training program, the shows and the webinars. Both firms are hands-on in every engagement; leads means owns the outcome and the quality.


Founders

Who you will be working with

AH
Founder, Fairway Systems

Aaron Henderson

Fairway Systems, what we do

Aaron founded Fairway in 2026 after a career building software platforms, most recently as a lead platform engineer for G2, a billion dollar software company, and running the design studio HelloSavvy. He read the rule end to end, built the fixed path through it, and put a plan behind every line on this site.

He is the person who answers the readiness call, and the reason every claim here carries its citation: he had to learn this rule from zero, so it is written the way he needed it explained.
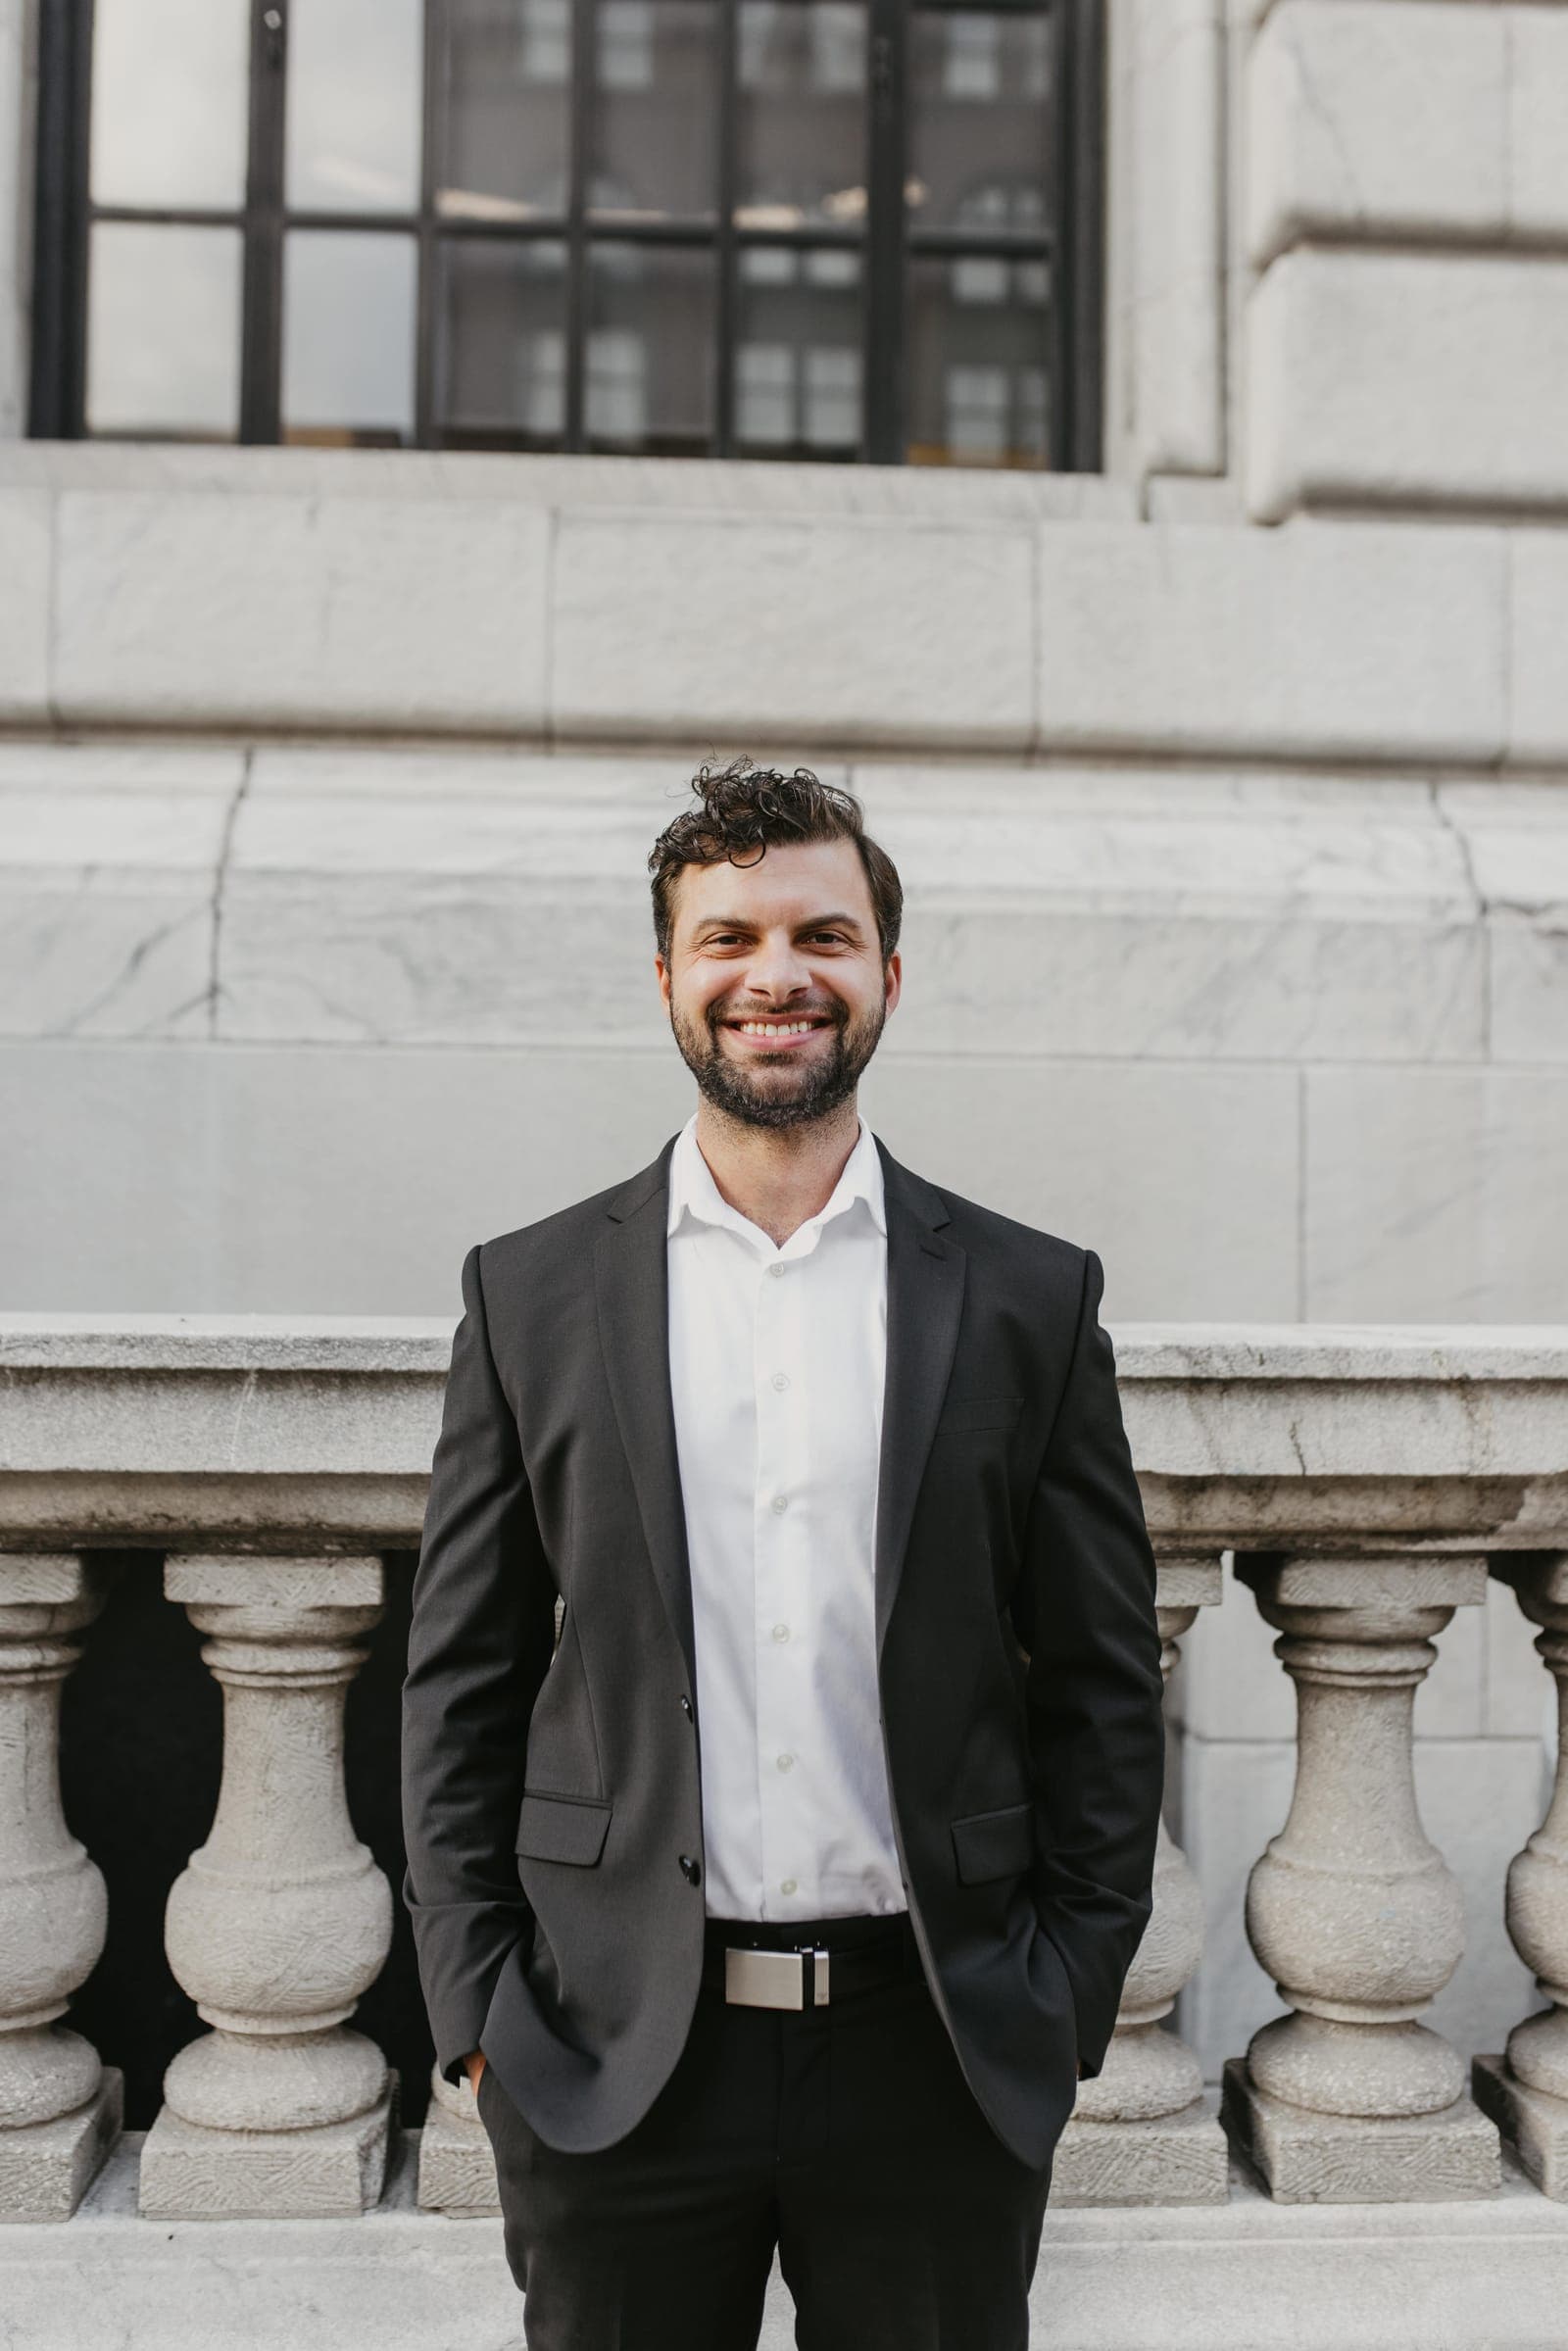
Bogdan Salamakha
Founder and CEO, Virtus Cybersecurity

Bogdan Salamakha

Virtus Cybersecurity, www.virtuscyber.com

Bogdan leads Virtus Cybersecurity, an independent security firm in North Royalton, Ohio, with over two decades in incident response, penetration testing and security architecture for Fortune 500 corporations, government agencies and startups.

He believes the best way to protect an organization is to teach it about the threats it faces, which is why he sits on every technical call and signs off every plan before it carries either firm's name.


About Virtus

An independent security firm, twenty years deep

Virtus Cybersecurity, LLC is an independent cybersecurity firm in North Royalton, Ohio: security assessments, penetration testing, incident response and digital forensics, security training and managed security. Its founder and CEO is Bogdan Salamakha.

What Virtus brings to this program is the part that cannot be learned from the rule text: finding what is actually exposed on a towboat's network or a terminal's control system, testing it, answering the phone when it goes wrong, and auditing the whole program with independent eyes.

www.virtuscyber.com


What this means for you

Simpler than what is behind it

One contract
You sign with Fairway. One fixed, itemized quote, one calendar, one number to call. The two-firm structure is ours to run, not yours to manage.
An audit that is independent by construction
The rule bars your Cybersecurity Officer from auditing their own measures. Ours cannot either, so the audit lane belongs to the firm that did not write the plan. That is how the service is built, not a favor arranged each year.
A bench behind the phone
When a vessel's network goes dark at two in the morning, the on-call officer has an incident response team behind them, not a voicemail.

Talk to the people who will run your program.

Thirty minutes, no charge. Bring your fleet and your questions; you leave with a written two-page readiness note and an honest read on where you stand.

Or call 303-848-9352 or email aaron@fairway.systems — a person answers within one business day.